
Bounty Program
ChainEX is a cryptocurrency exchange and as such security and protection of our system and platform is of the utmost importance to us. This Bug Bounty has been put in place in order to encourage the responsible disclosure of any bug or vulnerability contained within the ChainEX code or protocols and if any are found, to reward those who make such disclosures.
Bounty Policy
1. Application of legislation governing conduct:
ChainEX undertakes not to initiate legal action for security research conducted pursuant to all Bug Bounty Program policies or accidental violations, if the researcher fully complies with this Policy.
We will not bring a claim against researchers for circumventing the technological measures we have used to protect the applications in the scope of the Bug Bounty Program. Please understand that if your security research involves the networks, systems, information, applications, products or services of another party (which is not us), that third party may determine whether to pursue legal action. We cannot and do not authorize security research in the name of other entities.
Please submit an appropriately composed report before engaging in conduct that may be inconsistent with or unaddressed by this policy.
This report should include a brief description of your intended conduct so that we may determine whether it is consistent with the Bug Bounty Program policy.
ChainEX reserves the right to change or modify the terms of this program at anytime. You may not participate in this program if you are a person or entity identified on the TFS list. The searchable TFS list is available on the Financial Intelligence Centre (FIC) website (Pages - Home l Financial Intelligence Centre).
2. Confidentiality:
Any information you receive or collect about us, our affiliates, any of our users or employees in connection with the Bug Bounty Program (“Confidential Information”) must be kept confidential and only used in connection with the Bug Bounty Program.
You may not use, disclose or distribute any such Confidential Information, including without limitation any information regarding your submission, without our prior written consent. To protect the Confidential Information, you shall use all reasonable precautions required to be used for protection of such information and shall keep the Confidential Information, including documents and copies thereof containing Confidential Information, in a way preventing third parties’ unauthorized access thereto.
ChainEX does not give permission/authorization (either implied or explicit) to an individual or group of individuals to (1) extract personal information or content of ChainEX Users or publicize this information on the open or public-facing internet without ChainEX’s consent or (2) modify or corrupt data belonging to ChainEX in order to extract and publicly disclose data belonging to ChainEX.
All the Confidential Information is owned solely by ChainEX (or its licensors) and the unauthorized disclosure or use of such Confidential Information may cause irreparable harm and significant injury, the degree of which may be difficult to ascertain. Accordingly, we will have the right to pursue immediate legal action in the event of any breach of these provisions, as well as the right to pursue any and all other rights and remedies available in law or equity for such breach, including indemnity.
If you fail to protect the Confidential Information specified herein, and in case it is found out that the Confidential Information has been disclosed and/or misused, including, but not limited to, posting publicly (including on social media) materials with Confidential Information, content containing false and/or impairing goodwill, you shall be obliged to pay a fine in the amount of R1 000 000 (one million rand) to be accrued in addition to any damages incurred.
Notwithstanding the end of the term of your submission or closing the issue in connection with fixing and payment of remuneration, the provisions regarding Confidential Information will survive for ten (10) years after the Confidential Information has been received and, with respect to Confidential Information that constitutes a trade secret, for so long as such Confidential Information remains a trade secret.
3. Report requirements:
- Do not access customer or employee personal information. If you accidentally access any of these, please stop testing and submit the vulnerability.
- Stop testing and report the issue immediately if you gain access to any non-public application or credentials.
- Do not disrupt production systems, or destroy, or alter data during security testing.
- Collect only the information necessary to demonstrate the vulnerability.
- Include any necessary screenshots, screen captures, network requests, reproduction steps or similar in your submission (do not use third party file sharing sites).
- When investigating a vulnerability, please only target your own account and do not attempt to access data from anyone else’s account as this will contradict the ChainEX Terms of Use.
- When investigating a vulnerability, please avoid the destruction of data.
- You are not allowed to exploit a security vulnerability in any other way than prescribed in this Policy.
- Only the first verified vulnerability report can receive the reward.
4. To help streamline our intake process, we ask that submissions include:
- Vulnerability Types and Description of the vulnerability.
- Steps to reproduce the vulnerability.
- Proof of use (e.g. any necessary screenshots, screen captures or network requests).
- Vulnerability Exploitation Probability.
- List of URLs and affected payload parameters.
- Other additional payloads, evidence of vulnerability and solutions.
- Browser version, OS and/or app version used for testing.
Note: Failure to comply with these requirements or knowingly providing false information may result in ineligibility for a bounty and/or removal from the program.
5. Rights and licenses:
By making a submission, you give us the right to use your submission for any purpose. We may modify the Program Terms or cancel the Bug Bounty Program at any time.
6. Rewards:
ChainEX may, at its sole discretion, provide rewards to eligible reporters of qualified vulnerabilities. The reward will be paid in cryptocurrency into your ChainEX account, as ChainEX deems appropriate.
The value of rewards paid out will vary depending on Severity. The severity is calculated according to our risk rating model based on Impact and Probability.
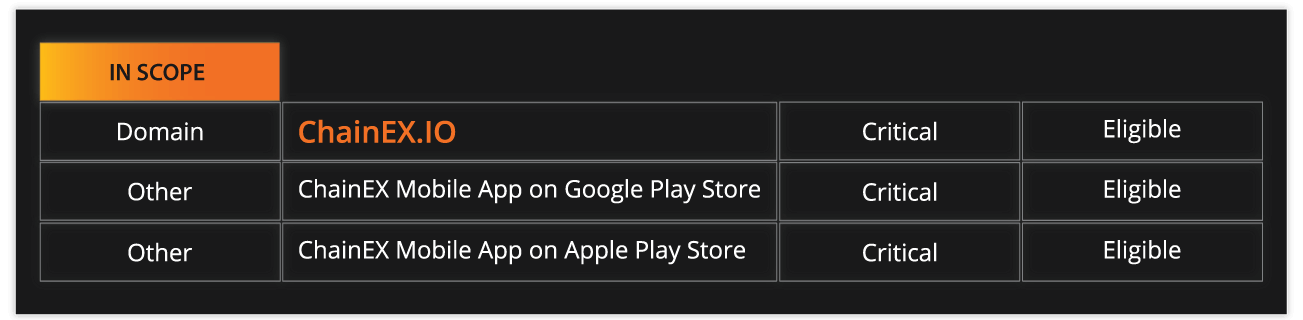
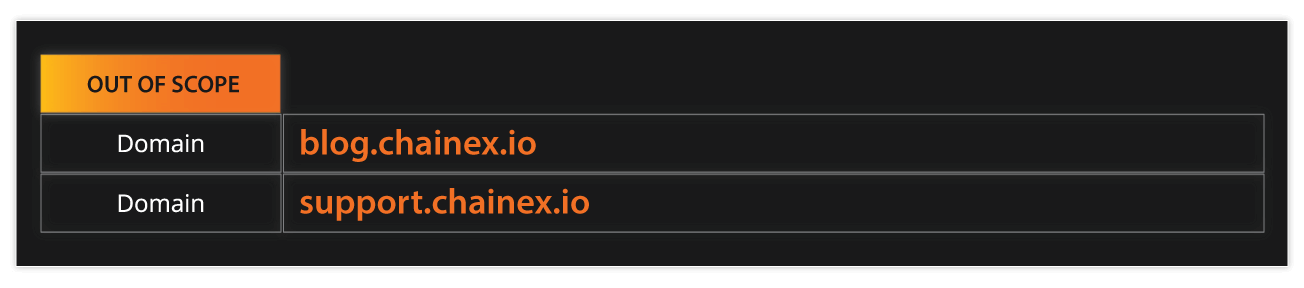
The following table outlines the nominal rewards for specific classes of vulnerabilities for in-scope properties (see the section on Scope).

7. The fine print:
A bounty will only be awarded to the first person who reports a vulnerability, unless two or more people report the same vulnerability at approximately the same time, in which case the bounty may be split between them.
- If the same vulnerability appears in multiple locations it will normally only receive a single bounty.
- Reports of security-related vulnerabilities are not eligible for bounties if the vulnerabilities are publicly disclosed prior to being fixed.
- Vulnerabilities need to be disclosed to the ChainEX team prior to receiving the bounty payment. The ChainEX team will not award a bounty payment upfront before knowing all details.
- Known upstream vulnerabilities, such as a bug in the Bitcoin or other Alt Coin's codebases or in one of the libraries used by ChainEX, do not qualify for bounty payment.
- The issue must be described in enough details to address it.
- Only the discoverer of a vulnerability is eligible for the associated bounty.
- All bounty claims need to be assessed individually on a case by case basis.
- Bounties will be confirmed and awarded within 10 days of their assessment by the ChainEX team.
- Inquiries on bounty status may be sent to support.
- Bounties will not be awarded if it is illegal to do so.
- The classification of vulnerabilities, values of bounties and conditions under which bounties are paid are subject to change without notice.
- The ChainEX team has sole discretion to determine whether a vulnerability report qualifies for a bounty and for which bounty it qualifies.
- If you have found a security issue that directly affects a cryptocurrency and/or its components (e.g. blockchain, node, wallet), please ensure that you report it directly to the respective project team.
8. Scopes
Log Vulnerability
If you believe you have found a vulnerability, please click the below button to submit the vulnerability. Do not post the issue on GitHub or anywhere else until the issue has been resolved.